Tuesday, July 2, 2013

Stolen credit cards... keep 'em. It's all about banking logins now

Crimeware-As-A-Service is a thing. Really.

Image source: Article
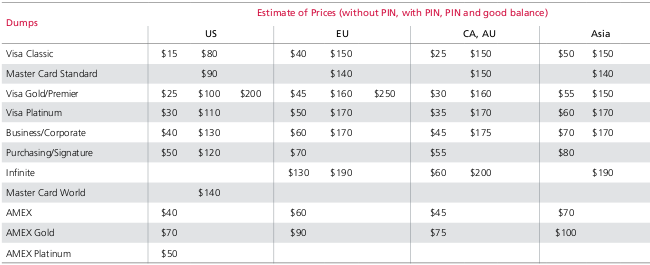
Stolen bank login information attracts an even higher price than credit card numbers on underground cybercrime bazaars.

The technical barrier to getting involved in cybercrime has been lowered thanks to various Cybercrime-As-A-Service offerings - including cybercrime-infrastructure-as-a-service, bulletproof hosting, password cracking and DDoS for hire offers.

What are your members' logins worth?

Thursday, May 30, 2013

Don’t Get Caught! Schedule a Surveillance System Spring Clean

You don’t have to go far these days to hear stories in which video surveillance plays a critical role in catching the bad guys.

Image source: Article
Unfortunately, we’ve also seen how an organization can end up with a huge — and costly — headache when its video surveillance system isn’t working properly.

To avoid getting caught in an embarrassing and potentially serious situation, I recommend a little spring cleaning of your video surveillance system.

Has your CU done its spring cleaning yet?

Monday, May 13, 2013

FBI says more cooperation with banks key to probe of cyber attacks

Bank security officers and others were brought to more than 40 field offices around the country to join a classified video conference on "who was behind the keyboards."

Image source: Article
The extraordinary clearances, from an agency famed for being close-mouthed even among other law enforcement agencies, reflect some action after years of talk about the need for increased cooperation between the public and private sectors on cybersecurity.

How has your CU been affected?

Monday, April 8, 2013

CU InfoSecurity Conference 2013 in Las Vegas

The Credit Union InfoSecurity Conference, the original and premier conference dedicated solely to credit union security, is holding its next summit on June 5-7, 2013 at the Platinum Hotel and Spa in Las Vegas.

Register for the event

Image source: imsmartin
The conference, which features industry leaders in their respective fields sharing their firsthand knowledge and practical advice on securing credit unions, is an incredible opportunity to gain new insight, network with credit union peers, and browse the Security Vendor Reception.

Possible topics to be covered at the upcoming summit include mobile security, data forensics, insider threats, incident response, social engineering, secure cloud storage, virtual desktop security, and fighting banking fraud.

If you are interested in attending the event, be sure to register here (https://www.cunews.com/infosecurity-conference.html).
Thursday, April 4, 2013

Gartner: Tablet shipments to outstrip PCs by 72% in 3 years

Three years from now, tablet computers will outsell traditional Windows PCs, and do so by a whopping 72%.

Image source: Article
Some of that decline will be made up by the faster growth in "ultramobiles," the new breed of Windows 8 devices such as Microsoft Surface Pro.

But the PC decline is permanent, reflecting a "long-term change in user behavior," according to the Gartner statement.

Where is your CU making your investment?

Monday, April 1, 2013

New malware goes directly to US ATMs and cash registers for card info

While many consumers already take precautions when shopping online, they may need to start being even more careful - as a new report shows malware is focusing on physical registers and ATMs compromised by attackers looking to harvest card data.

Image source: Article
The malicious code is evidently being installed directly into point-of-sale (POS) hardware (meaning registers or kiosks) and ATMs, and transmitting the harvested information straight out of the magnetic stripes on credit and debit cards - which includes everything from account numbers, to first and last names and expiration dates.

Are your CU's ATMs secure?

Friday, March 29, 2013

Google Chrome: Best security tips for safer browsing

There's a lot to like about Google Chrome's built-in security features.

Image source: Article
The browser offers unique sandboxing functions and privilege restrictions, and even updates itself in the background to help better protect you from hackers and malware.

But like all browsers, Chrome is imperfect, and there are steps you can take to protect it from attack.

Read the full article to see how to get the most from Chrome's built-in security features, and work around its security shortcomings.

Tuesday, March 26, 2013

Wells Fargo bank site attack disrupts service

Wells Fargo's online banking site was experiencing problems Tuesday, with a denial-of-service attack.

Image source: Article
This attack likely the reason behind the slowdowns for some customers trying to access the site.

This isn't the first time the bank site has been under a denial-of-service attack, where hackers inundate a website with traffic to delay or disrupt it.

Think your CU is safe? Think again.

Risk management becoming focus of bank boards

The majority of the boards of directors for large banks are spending significantly more time on risk management, according to a new survey.

Image source: Article
The survey, which was conducted in January using risk officers and directors at banks with more than $5 billion in assets, said 91 percent of those surveyed reported an increase in time devoted to risk management issues within board meetings over the last three years.

Seventy-two percent of risk officers and 63 percent of directors report that this time has doubled or tripled.

What is your board's position on risk management?

Monday, March 25, 2013

Hackers Set Time Bomb to Damage Targeted Banks and Broadcasters

The AhnLab Security Emergency Response Center (ASEC) and US headquarters of South Korea-based AhnLab confirmed a large series of cyber attacks that targeted banks and broadcasters in South Korea.

Image source: chaitanyak.deviantART
AhnLab said that attackers used stolen user IDs and passwords to launch some of the attacks.

The credentials were used to gain access to individual patch management systems located on the affected networks.

Does your CU have control over your patch management system?

Mobile location data 'present anonymity risk'

Scientists say it is remarkably easy to identify a mobile phone user from just a few pieces of location information.

Image source: Article
But a study in Scientific Reports warns that human mobility patterns are so predictable it is possible to identify a user from only four data points.

Recent work has increasingly shown that humans' patterns of movement, however random and unpredictable they seem to be, are actually very limited in scope and can in fact act as a kind of fingerprint for who is doing the moving.

Does your CU let its employees use location features on their smartphones?

Wednesday, March 20, 2013

Internet Explorer 8 Exploit Found in Watering Hole Campaign Targeting Chinese Dissidents

On March 16th, FireEye discovered a premeditated waterhole campaign that hosts exploits and malware on websites frequented by a specific target group.

Image source: Article
The attack exploits a fresh vulnerability (CVE-2013-1288, MS13-021) in Internet Explorer 8—just four days after Microsoft released a patch.

Why did attackers use a fresh vulnerability? Cost could be a factor. Zero-days tend to be expensive to either research or purchase on black markets.

Has your CU applied this patch?

Tuesday, March 19, 2013

Free Android malware analysis tool

Bluebox Labs announced Dexter, a free tool to help researchers and enterprise security teams analyze applications for malware and vulnerabilities.

Image source: Article
The increasing popularity of the Android platform has resulted in an explosion of applications, but with shortened development cycles, many are released without proper security analysis.

This often leads to undetected malware making it to market along with the app.

Does your CU worry about mobile malware?

Monday, March 18, 2013

Increased spy access to Americans' banking data raises privacy concerns

Spy agencies like the CIA and NSA would have access to a database used to fight domestic financial crime under a proposal being drafted by the Obama Administration.

Image source: Article
The database, among other things, catalogs bank deposits of $10,000 or more made by American citizens and anyone else doing business with a U.S. bank.

Opening up the federal database, known as the Financial Crimes Enforcement Network (FinCEN), to more government eyes would be a mistake, said J . Bradley Jansen, director of the Center for Financial Privacy and Human Rights (CFPHR) in Washington, D.C.

What is your CU's position on this topic?

Friday, March 15, 2013

3G and 4G USB modems are a security threat, researcher says

The vast majority of 3G and 4G USB modems handed out by mobile operators to their customers are manufactured by a handful of companies and run insecure software, according to two security researchers from Russia.

Image source: Wikimedia
Researchers showed how to attack the 3G and 4G USB modems at Black Hat Europe.

The researchers tested the software preloaded on the modems and found multiple ways to attack it or to use it in attacks.

How many USB modems does your CU use?

House Oversight Committee floats FISMA update

The leadership of the House Oversight and Government Reform Committee introduced a bill on March 14 to update federal information security regulations.

Image source: Article
The updated regulations are likely to include continuous monitoring of cybersecurity threats and regular threat assessments.

This update to FISMA will incorporate the last decade of technological innovation, while also addressing FISMA shortcomings realized over the past years.

Does your CU have to follow these rules?

Wednesday, March 13, 2013

The Dingo and the Baby

FireEye has been tracking an APT campaign for a while and we have noticed that this attack is currently active and targeting companies.

Image source: Article
In this case, the campaign uses the name of the company it targets in the CnC domain name.

What does this have to do with dingoes and babies? The title comes from a string that we saw in all of the malware, called LetsGo/Merong, and its variants.

Do you know where the dingo is?

Tuesday, March 12, 2013

Big Data Raises Authenticity Concerns

Big data is literally everywhere. It’s in the cloud and under the cloud, at rest and on the move, and growing at a mind-boggling rate.

Image source: Guardtime
IBM, a leader in big data analytics, has estimated that organizations create 2.5 quintillion bytes of data each day — and that 90 percent of the data in the world has been created in the last two years alone.

Thanks to cloud computing, petabytes of unstructured data are created daily online and much of this information has an intrinsic business value if it can be captured and analyzed.

Does your CU have big data security issues?

Friday, March 8, 2013

RSA 2013 The Age Of Security Commercialism

Walking on the RSA 2013 show floor, it was a chaotic, noisy, and energetic place, pulsing with excitement.

Image source: Article
The week heading to the conference was interesting to say the least; with Java 0-days wreaking havoc on the Internet and the Mandiant report taking every major newspaper headline, RSA could not have had a better set-up.

After the dust (and the smoke) settled, the Forrester security team came away with a number of unique impressions and takeaways.

Read the full article to learn more.

Wednesday, March 6, 2013

SharePoint 2013 Challenges and Questions for CIOs

SharePoint 2013 arrives with a new user interface and new collaboration, search, storage and task management features.

Image source: Article
But gaps remain in areas like social and mobile, and upgrading and governing SharePoint is still rife with challenges.

Good Technology's GoodShare is part of a comprehensive mobile collaboration solution which brings SharePoint & NAS to the financial industry.

Does your CU want SharePoint on mobile?